
Phone calls are sensitive. We treat them that way.
Vistrow Voice handles recordings, transcripts, and personal details captured on live calls. This page lists the controls that exist today - and, at the bottom, the ones that don’t yet.
- No signup needed
- 5 free calls
- 130+ languages
What protects call data today.

Workspace isolation
Dashboard queries for calls, contacts, agents, recordings, and knowledge bases are scoped to the authenticated workspace. Access-control defects are treated as security incidents and investigated promptly.

Credential handling
Passwords are stored only as salted hashes, never in readable form. Sessions use signed, expiring tokens in HTTP-only cookies. API keys are shown once, then stored hashed, and can be revoked at any time.

Role-based access
Team members are invited into your workspace with a role. Compliance settings, API keys, integrations and team management need an admin or owner role.

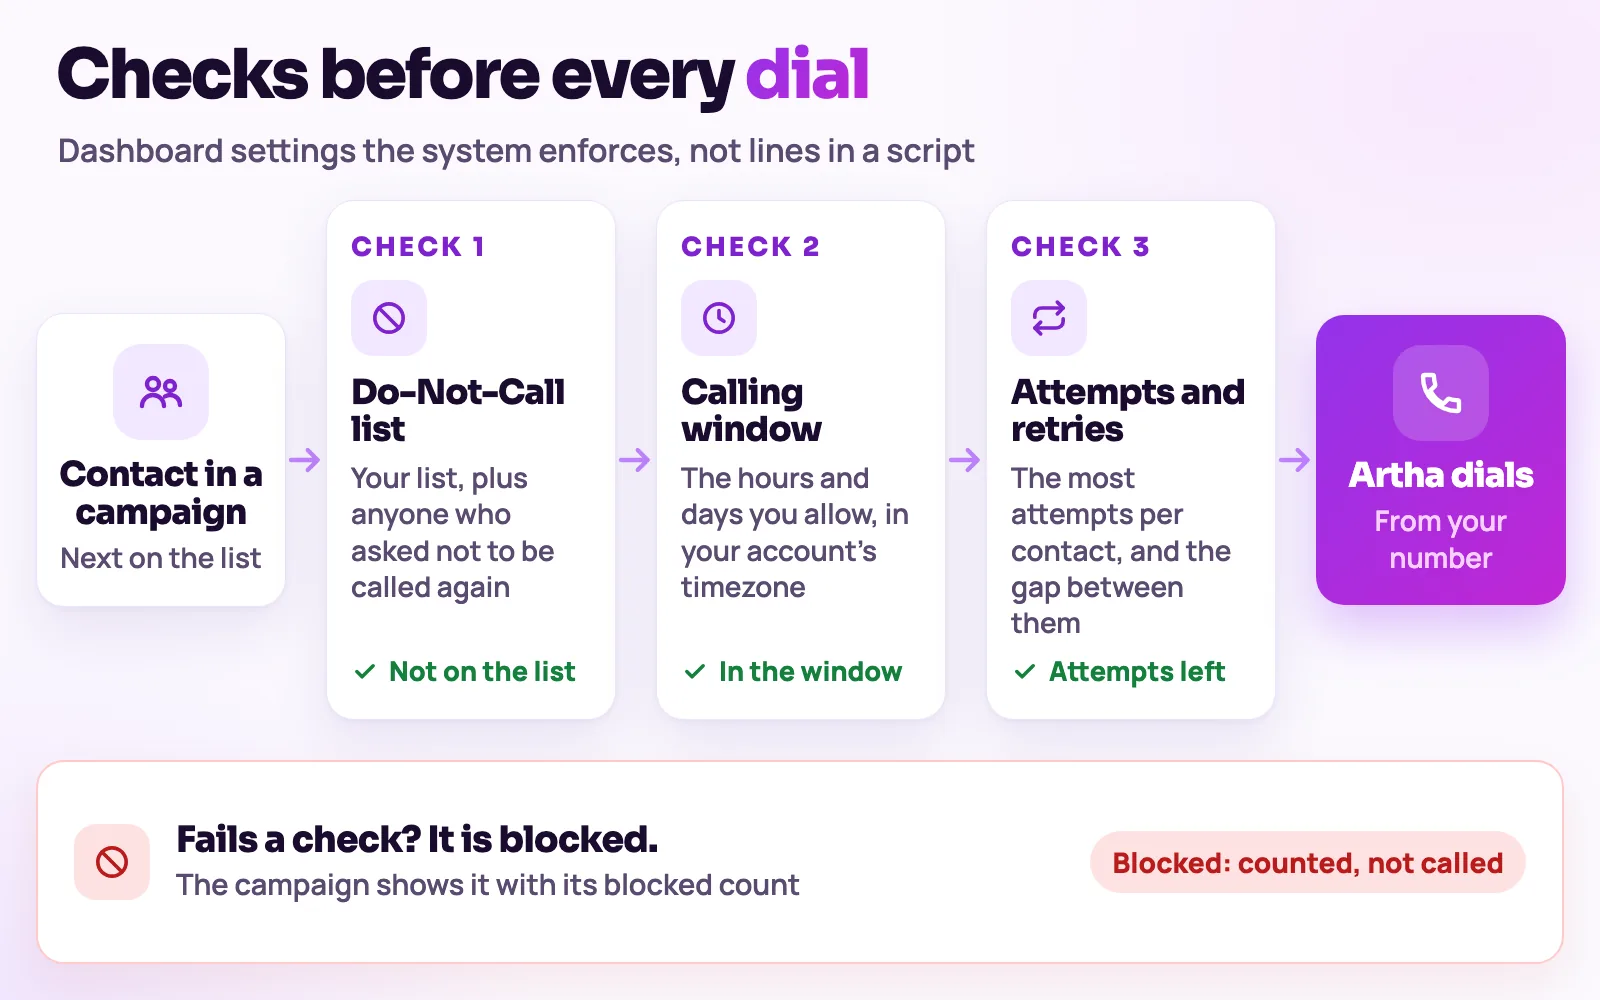
Do-Not-Call enforcement
Your DNC registry is a hard block checked before any outbound dial leaves the platform. A blocked number is never dialled - a call can’t be un-rung, so the gate runs first.

Calling-window rules
Outbound calling is restricted to the hours and days you configure. Dials attempted outside that window are refused and logged rather than placed.

Configurable retention
Set a retention period and call records older than it are purged automatically - data minimisation under the DPDP Act rather than keeping everything forever by default.

Recording access control
Recordings sit in private storage with no public address. Dashboard playback uses one-hour signed URLs issued to signed-in members of the owning workspace. Recording links sent to a connected CRM or spreadsheet work for anyone who holds them until they expire (90 days by default, configurable), are revoked by a workspace admin, or the recording is deleted. Links sent before link expiry was introduced in October 2026 last until revoked.

No vendor surface
Our agents are built to decline questions about the underlying models and speech stack. Your callers - and your competitors - can’t extract our architecture from a conversation.

No card data
Card details are entered with Razorpay, our payment provider. We store only invoice and payment identifiers, never card numbers.
Your data stays yours.
You are the controller
You decide who gets called, what the agent says, what it captures, and how long any of it is kept. Recordings, transcripts, and lead data belong to your business.
We are the processor
We process that data to run the service you configured - nothing else. We don’t sell it, and we don’t use your call content to train models for other customers.
The full legal detail lives in our Privacy Policy and Terms.
Controls that run on every call.
Each of these is a setting or a rule in the product today, listed in full above.
Workspace isolation
Calls, contacts, agents, recordings and knowledge bases are scoped to your workspace.
Do-Not-Call enforcement
Checked before any outbound dial leaves the platform.
Configurable retention
Records older than your retention period are purged automatically.
No card data
Card details are entered with our payment provider, never stored by us.
The gaps, stated plainly.
Plenty of vendors imply certifications they don’t hold. We’d rather you find out here than in a procurement review.
- A formal SOC 2 Type II audit - not yet started; we will publish the report when it exists rather than implying it now.
- India-region data residency - call data is currently processed and stored outside India. If in-country residency is a requirement for you, tell us before you sign so we can be straight about timelines.
- A published third-party penetration-test summary.
Found a vulnerability?
Report it to us privately and we’ll acknowledge it. Please don’t test against live tenant data or place real calls as part of any testing.
Report a security issuePut an AI agent on every call.
Try Artha live in your browser, or book a walkthrough with our team.
- No signup needed
- 5 free calls
- 130+ languages